

- Joined
- Dec 30, 2024
- Messages
- 396
- Reaction score
- 208
- Points
- 62
- Website
- blackhatpakistan.net
- Points
- 1,108
- USD
- 1,108
An Aircrack-ng tutorial walks the full wireless audit workflow: put the adapter in monitor mode (airmon-ng), survey the air (airodump-ng), capture a target's WPA2 4-way handshake (aireplay-ng to provoke one), then crack it against a wordlist (aircrack-ng). The suite is four tools sharing one job - and the handshake capture is the crux, because WPA2 never sends a reusable password over the air; you are collecting the cryptographic exchange and testing candidates against it offline.
TL;DR - airmon-ng (monitor mode) -> airodump-ng (survey + capture) -> aireplay-ng (deauth to force the handshake) -> aircrack-ng (offline wordlist crack). The capture needs the full 4-way EAPOL exchange for the target AP and client. PMKID capture is the no-client alternative. Cracking speed depends on the wordlist and rules, not on the capture - a perfect handshake with a bad dictionary never cracks.
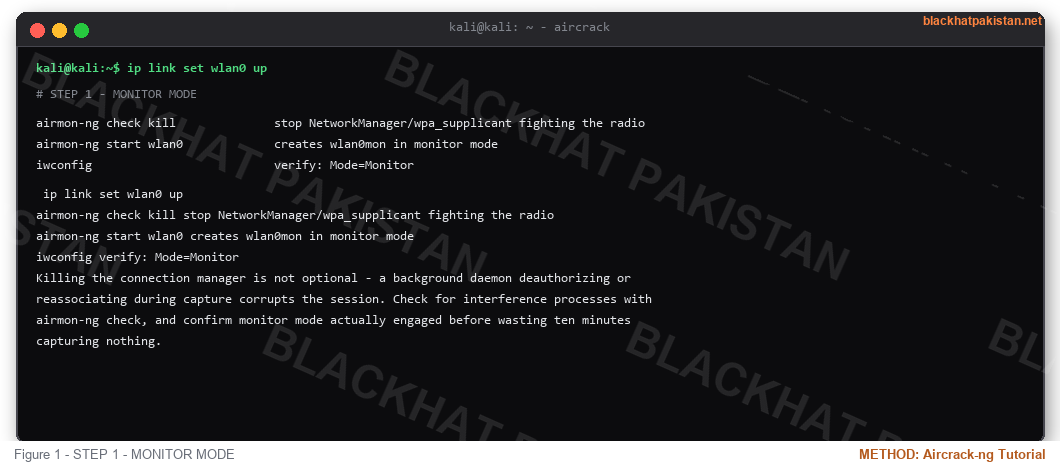
STEP 1 - MONITOR MODE
Killing the connection manager is not optional - a background daemon deauthorizing or reassociating during capture corrupts the session. Check for interference processes with airmon-ng check, and confirm monitor mode actually engaged before wasting ten minutes capturing nothing.
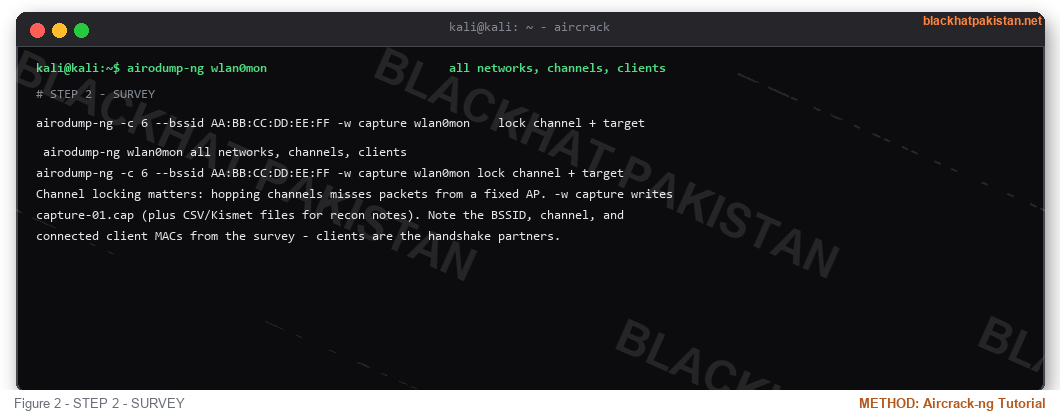
STEP 2 - SURVEY
Channel locking matters: hopping channels misses packets from a fixed AP. -w capture writes capture-01.cap (plus CSV/Kismet files for recon notes). Note the BSSID, channel, and connected client MACs from the survey - clients are the handshake partners.
STEP 3 - FORCE THE HANDSHAKE
The deauthentication is a management-frame disconnection: the client's supplicant immediately re-associates and the reassociation carries the EAPOL 4-way handshake the capture is waiting for. APs with client isolation or protection bits may ignore injected frames - the fallback is passive waiting for a natural reconnect (any reboot, rebooting phone, or laptop wake produces one). PMKID capture avoids the client entirely: some APs hand over a PMKID in the first message, captured without any deauth at all.
Every guess re-derives the key from the passphrase plus the SSID salt - which is why SSID-specific rainbow tables work only for common SSIDs, and why a unique SSID forces pure dictionary attack.
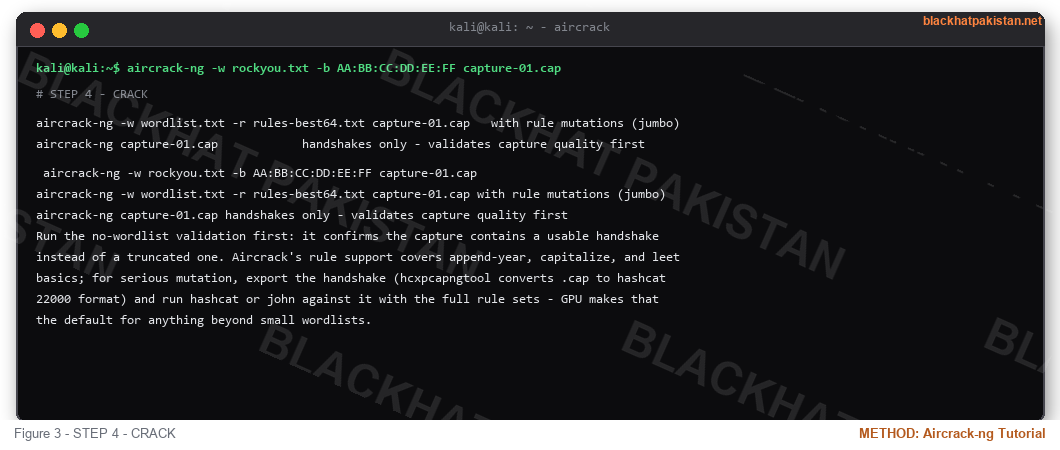
STEP 4 - CRACK
Run the no-wordlist validation first: it confirms the capture contains a usable handshake instead of a truncated one. Aircrack's rule support covers append-year, capitalize, and leet basics; for serious mutation, export the handshake (hcxpcapngtool converts .cap to hashcat 22000 format) and run hashcat or john against it with the full rule sets - GPU makes that the default for anything beyond small wordlists.
CAPTURE QUALITY PROBLEMS
- Truncated handshake - missed message 2 or 3 of the exchange. Deauth again with the client in frame range.
- Wrong BSSID - hidden SSIDs and probe-response confusion lead captures at the wrong AP. Match BSSID from the survey, always.
- Multiple handshakes mixed in one cap - fine; tools pick valid ones, but keep captures per-target for clean reporting.
- Low signal / distant client - packets drop at the adapter. Capture from range with the client visible, or use PMKID.
- PMF (802.11w) - management-frame protection blocks deauth injection. PMKID or natural reconnect are the remaining paths.
FAQ
Q: Do I need a client connected?
A: For the classic 4-way handshake, yes - it is a conversation between AP and client. PMKID captures work with no client present if the AP includes it in message 1.
Q: Why does aircrack find nothing when the password is in my list?
A: Ninety percent is capture quality (validate first), ten percent is list format - one password per line, correct encoding, no duplicate whitespace. The password itself being present always cracks.
Q: What wireless security holds up against this workflow?
A: WPA3's SAE handshake removes offline dictionary testing entirely (and protected management frames remove the deauth lever). On WPA2, long unique passphrases are the practical defense - the capture succeeds regardless of password length; the guessing does not.
Q: How is this seen in authorized testing?
A: Wireless assessments are scoped engagements: monitor-mode scanning within the client's premises, handshake capture as proof of PSK weakness, offline cracking attempts against the scope's own handshake. Deauth frames inside the scope are a standard technique; anywhere outside written authorization they are interference with someone else's equipment.
RELATED ON BLACKHAT PAKISTAN
Nmap Cheat Sheet 2026 - mapping the network the access point sits on.
John the Ripper - rule sets and format handling for the offline crack.
Hydra Brute Force Tutorial 2026 - the online-guessing counterpart once inside.
Kali Linux Tools List 2026 - where the wireless suite sits in the toolkit.
TL;DR - airmon-ng (monitor mode) -> airodump-ng (survey + capture) -> aireplay-ng (deauth to force the handshake) -> aircrack-ng (offline wordlist crack). The capture needs the full 4-way EAPOL exchange for the target AP and client. PMKID capture is the no-client alternative. Cracking speed depends on the wordlist and rules, not on the capture - a perfect handshake with a bad dictionary never cracks.
STEP 1 - MONITOR MODE
Code:
ip link set wlan0 up

airmon-ng check kill              stop NetworkManager/wpa_supplicant fighting the radio

airmon-ng start wlan0             creates wlan0mon in monitor mode

iwconfig                          verify: Mode=Monitor
Killing the connection manager is not optional - a background daemon deauthorizing or reassociating during capture corrupts the session. Check for interference processes with airmon-ng check, and confirm monitor mode actually engaged before wasting ten minutes capturing nothing.
STEP 2 - SURVEY
Code:
airodump-ng wlan0mon                          all networks, channels, clients

airodump-ng -c 6 --bssid AA:BB:CC:DD:EE:FF -w capture wlan0mon    lock channel + target
Channel locking matters: hopping channels misses packets from a fixed AP. -w capture writes capture-01.cap (plus CSV/Kismet files for recon notes). Note the BSSID, channel, and connected client MACs from the survey - clients are the handshake partners.
STEP 3 - FORCE THE HANDSHAKE
Code:
aireplay-ng -0 10 -a AA:BB:CC:DD:EE:FF -c 11:22:33:44:55:66 wlan0mon

# -0 = deauth count, -a = AP, -c = client - the client reconnects, full 4-way exchange follows
The deauthentication is a management-frame disconnection: the client's supplicant immediately re-associates and the reassociation carries the EAPOL 4-way handshake the capture is waiting for. APs with client isolation or protection bits may ignore injected frames - the fallback is passive waiting for a natural reconnect (any reboot, rebooting phone, or laptop wake produces one). PMKID capture avoids the client entirely: some APs hand over a PMKID in the first message, captured without any deauth at all.
Code:
WPA2 handshake = ANonce, SNonce, MIC, AP and client MACs

candidate password -> PBKDF2 (4096 rounds, SSID as salt) -> PMK

PMK + both nonces -> PTK -> MIC check = match or no match
Every guess re-derives the key from the passphrase plus the SSID salt - which is why SSID-specific rainbow tables work only for common SSIDs, and why a unique SSID forces pure dictionary attack.
STEP 4 - CRACK
Code:
aircrack-ng -w rockyou.txt -b AA:BB:CC:DD:EE:FF capture-01.cap

aircrack-ng -w wordlist.txt -r rules-best64.txt capture-01.cap   with rule mutations (jumbo)

aircrack-ng capture-01.cap            handshakes only - validates capture quality first
Run the no-wordlist validation first: it confirms the capture contains a usable handshake instead of a truncated one. Aircrack's rule support covers append-year, capitalize, and leet basics; for serious mutation, export the handshake (hcxpcapngtool converts .cap to hashcat 22000 format) and run hashcat or john against it with the full rule sets - GPU makes that the default for anything beyond small wordlists.
CAPTURE QUALITY PROBLEMS
- Truncated handshake - missed message 2 or 3 of the exchange. Deauth again with the client in frame range.
- Wrong BSSID - hidden SSIDs and probe-response confusion lead captures at the wrong AP. Match BSSID from the survey, always.
- Multiple handshakes mixed in one cap - fine; tools pick valid ones, but keep captures per-target for clean reporting.
- Low signal / distant client - packets drop at the adapter. Capture from range with the client visible, or use PMKID.
- PMF (802.11w) - management-frame protection blocks deauth injection. PMKID or natural reconnect are the remaining paths.
FAQ
Q: Do I need a client connected?
A: For the classic 4-way handshake, yes - it is a conversation between AP and client. PMKID captures work with no client present if the AP includes it in message 1.
Q: Why does aircrack find nothing when the password is in my list?
A: Ninety percent is capture quality (validate first), ten percent is list format - one password per line, correct encoding, no duplicate whitespace. The password itself being present always cracks.
Q: What wireless security holds up against this workflow?
A: WPA3's SAE handshake removes offline dictionary testing entirely (and protected management frames remove the deauth lever). On WPA2, long unique passphrases are the practical defense - the capture succeeds regardless of password length; the guessing does not.
Q: How is this seen in authorized testing?
A: Wireless assessments are scoped engagements: monitor-mode scanning within the client's premises, handshake capture as proof of PSK weakness, offline cracking attempts against the scope's own handshake. Deauth frames inside the scope are a standard technique; anywhere outside written authorization they are interference with someone else's equipment.
RELATED ON BLACKHAT PAKISTAN
Nmap Cheat Sheet 2026 - mapping the network the access point sits on.
John the Ripper - rule sets and format handling for the offline crack.
Hydra Brute Force Tutorial 2026 - the online-guessing counterpart once inside.
Kali Linux Tools List 2026 - where the wireless suite sits in the toolkit.
Last edited:


